Guaranteed Accomplishment with Newest Jan-2024 FREE Microsoft MS-101 [Q36-Q53]

Guaranteed Accomplishment with Newest Jan-2024 FREE Microsoft MS-101 [Q36-Q53]

5/5 - (2 votes)

Guaranteed Accomplishment with Newest Jan-2024 FREE Microsoft MS-101

Use Valid New Free MS-101 Exam Dumps & Answers

Q36. Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1.
Your company purchases a Microsoft 365 subscription.
You need to ensure that User1 is assigned the required role to create file policies and manage alerts in the Cloud App Security admin center.
Solution: From the Security & Compliance admin center, you assign the Security Administrator role to User1.
Does this meet the goal?


Q37. You have a Microsoft 365 subscription.
You have the devices shown in the following table.

You plan to join the devices to Azure Active Directory [Azure AD)
What should you do on each device to support Azure AU join? To answer, drag the appropriate actions to the collect devices, Each action may be used once, more than once, of not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

Q38. You need to ensure that User1 can enroll the devices to meet the technical requirements. What should you do?


Q39. You have a Microsoft 365 tenant that contains 100 Windows 10 devices. The devices are managed by using Microsoft Endpoint Manager.
You plan to create two attack surface reduction (ASR) policies named ASR1 and ASR2. ASR1 will be used to configure Microsoft Defender Application Guard. ASR2 will be used to configure Microsoft Defender SmartScreen.
Which ASR profile type should you use for each policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q40. You have a Microsoft 365 tenant that is signed up for Microsoft Store for Business and contains the users shown in the following table.
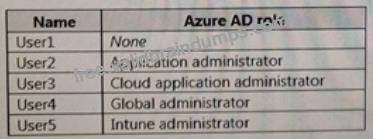
All users have Windows 10 Enterprise devices.
The Products & services settings in Microsoft Store for Business are shown in the following exhibit.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q41. You have a Microsoft 365 tenant that contains devices enrolled in Microsoft Intune. The devices are configured as shown in the following table.

You plan to perform the following device management tasks in Microsoft Endpoint Manager:
Deploy a VPN connection by using a VPN device configuration profile.
Configure security settings by using an Endpoint Protection device configuration profile.
You need to identify which devices will support the management tasks.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q42. You need to meet the technical requirement for large-volume document retrieval.
What should you create?


Q43. Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these
questions will not appear in the review screen.
You are deploying Microsoft Intune.
You successfully enroll Windows 10 devices in Intune.
When you try to enroll an iOS device in Intune, you get an error.
You need to ensure that you can enroll the iOS device in Intune.
Solution: You configure the Apple MDM Push certificate.
Does this meet the goal?


Q44. Your company has 5,000 Windows 10 devices. All the devices are protected by using Microsoft Defender Advanced Threat Protection (ATP).
You need to create a filtered view that displays which Microsoft Defender ATP alert events have a high severity and occurred during the last seven days.
What should you use in Microsoft Defender ATP?


Q45. You have a Microsoft 365 subscription.
In the Exchange admin center, you have a data loss prevention (DLP) policy named Policy1 that has the following configurations:
Block emails that contain financial data.
Display the following policy tip text: Message blocked.
From the Security & Compliance admin center, you create a DLP policy named Policy2 that has the following configurations:
Use the following location: Exchange email.
Display the following policy tip text: Message contains sensitive data.
When a user sends an email, notify the user if the email contains health records.
What is the result of the DLP policies when the user sends an email? To answer, drag the appropriate results to the correct scenarios. Each result may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

Q46. You have a Microsoft Azure Activity Directory (Azure AD) tenant contains the users shown in the following table.

Group3 is a member of Group1.
Your company uses Windows Defender Advanced Threat Protection (ATP). Windows Defender ATP contains the roles shown in the following table.

Windows Defender ATP contains the device groups shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q47. You have a Microsoft 365 subscription that contains the alerts shown in the following table.

Which properties of the alerts can you modify?


Q48. You have a Microsoft 365 subscription.
You have the devices shown in the following table.
You need to onboard the devices to Windows Defender Advanced Threat Protection (ATP). The solution must avoid installing software on the devices whenever possible.

Which on boarding method should you use for each operating system? To answer, drag the appropriate methods to the correct operating systems, Each method may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content NOTE: Each correct selection is worth one point.

Q49. You have the Microsoft Azure Active Directory (Azure AD) users shown in the following table.

Your company uses Microsoft Intune.
Several devices are enrolled in Intune as shown in the following table.

You create a conditional access policy that has the following settings:
The Assignments settings are configured as follows:
* Users and groups: Group1
* Cloud apps: Microsoft Office 365 Exchange Online
* Conditions: Include All device state, exclude Device marked as compliant Access controls is set to Block access.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q50. You have a data loss prevention (DIP) policy.
You need to increase the likelihood that the DLP policy will apply to data that contains medical terms from the International Classification of Diseases (ICD-9-CM). The solution must minimize the number of false positives.
Which two settings should you modify? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.

Q51. You need to meet the technical requirements and planned changes for Intune.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q52. Your company has a Microsoft 365 subscription.
You need to configure Microsoft 365 to meet the following requirements:
* Malware found in email attachments must be quarantined for 20 days.
* The email address of senders to your company must be verified.
Which two options should you configure in the Security & Compliance admin center? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q53. You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
A user named User1 has files on a Windows 10 device as shown in the following table.

In Azure Information Protection, you create a label named Label1 that is configured to apply automatically. Label1 is configured as shown in the following exhibit.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.


MS-101 Braindumps PDF, Microsoft MS-101 Exam Cram: https://www.validbraindumps.com/MS-101-exam-prep.html


Related Links: myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below